

Vulnerability Management Isn't About the Score — It's About How It Applies to You
Organizations need to move away from vendor-assigned, theoretical scores toward real exploit data specific to their environments.

⭐ Favourites
Updated 2 min ago · 50 articles from Dark Reading
Organizations need to move away from vendor-assigned, theoretical scores toward real exploit data specific to their environments.
Hundreds of stores lost millions of euros because they hired third parties to manage the outdated OT firmware running their cooling systems.

CVE-2026-104935, a high-severity authentication bypass + RCE vulnerability, was only partially discovered and patched in July, leaving an opening for threat ...
A sprawling cybercrime marketplace supplied cloud infrastructure and phishing kits that helped fuel more than 1 billion phishing messages worldwide.
A bug in Claude Code Desktop's preview pane can allow adversaries to quietly steal credentials from developers, including SSH private keys, AWS credentials, ...
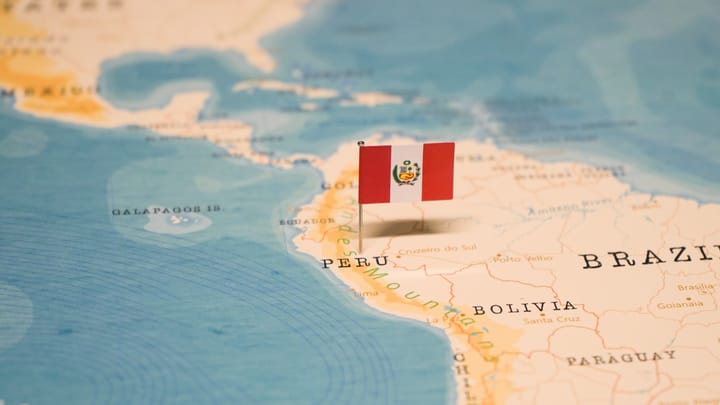
The AI-enabled operation used spoofed emails, fake government documents, and the creation of a local organization to target schools in Peru and Ecuador, amon...
Organizations are reporting that employees face threats of stalking, physical violence, and abduction. But these alarming claims are hard to verify.

The scary surprises in the largest security update ever include defense bypasses and unauthenticated RCEs.
The Democratic People's Republic of Korea (DPRK) is trying to get insight into its own war effort in Ukraine, through simple reply-baiting phishing attacks.
Anthropic's latest study combines IoT and network tests to explore AI self-replication, which researchers said would be "challenging" to shut down.

Attackers are currently targeting a critical vulnerability in SMA 1000 appliances, putting SonicWall customers in a familiar yet unenviable position.
Edward Dubrovsky, a longtime cybersecurity executive, was arrested and charged in Pennsylvania last week under conspiracy to extort money.
